Ghideon
Senior Members
-
Joined
Everything posted by Ghideon
-
A password salt is a unique, random string of data added to a plaintext password before it is run through a cryptographic hash function. The salt is stored together with the hashed value for (password+salt). The hash function is one-way, there is no feasible algorithm that can retrieve the original password from the hash. When logging in, the system takes the stored salt, combines it with the entered password, hashes it again, and compares this hash value to the stored hash value. Without salt an attacker can retrieve the list of hashed passwords from a system and use a list of hashes (a "rainbow table") for common passwords and run a comparison. With salt generic precomputed tables are ineffective because each password has a unique salt so the attacker must recompute guesses separately per account. Note that salting is about hashing, rather than reversible encryption. Yes, that is the point with public key encryption. Establishing the identity of the communicating parties is already an integrated part of currently established protocols and commonly used public key infrastructures. Openssl was shown above and here is a command to verify identities, in this case www.scienceforums.net host=www.scienceforums.net openssl s_client \ -connect "$host:443" \ -servername "$host" \ -showcerts \ -verify_return_error \ -verify_hostname "$host" </dev/nullFor testing and education badssl.com provides intentionally incorrect settings. Example: Use the above command with the following host to see that you get a "hostname mismatch" wrong.host.badssl.com (I think a complete explanation of certificate chains, issuers, trusted root certificates etc is off topic here)
-
In my opinion parallells between the Potter universe and LLMs like those in ChataGPT are more obvious in the Chamber of Secrets than in Prisoner of Azkaban. After a misadventure, that includes a flying Ford Anglia, Ron Weasley's wand malfunctions and starts to mimic an LLM; when prompted to produce something useful it often spits out crazy sh*t.
-
Good point! I could have clarified the separation. In real application of public key encryption there are complete ecosystems, Public Key Infrastructure (PKI). trurl's posts mixes cryptographic concepts (for instance encryption/decryption) and infrastructure concepts (key generation, key exchange etc). I think the following clarifies: And as you say there are other vulnerabilities related to this, beyond attacks based mathematical properties.
-
missed that one; simple: Eve impersonates Caesar during key distribution and gives Alice Eve's public key while claiming it belongs to Caesar. Alice then encrypts using Eve's key, for which Eve has the corresponding private key. How does Alice authenticate that the public key actually belongs to Caesar? In established public key cryptographic protocols this problem is well-known and solutions exist.
-
I did read the article* and no such thing is mentioned. As pointed out by several members above you have no working protocol for encryption. The receiver gets a message that is ambiguous. In Gematria different texts can produce the same numerical value and this can be used to imply mysterious connections or meanings, I suggest you open a thread in religion of this is you area of interest. In computing a related concept is "hash collision"**. Hash functions and cryptographic hash functions have many uses, for instance in relation to protecting sensitive information. There are interesting mathematical aspects better left for some other thread. *) https://en.wikipedia.org/wiki/Gematria Edited on 26 August 2026 21:04 (utc) **) https://en.wikipedia.org/wiki/Hash_collision
-
Caesar now have two private keys. Gematria is a concept from numerology (not cryptology). I begin to think this was posted in the wrong section…
-
The newest post doesn't answer earlier objections, and: Two parties need one private key each to be able to communicate bidirectional. For sending messages in one direction then only the receiver needs their private key to decrypt incoming messages that was encrypted using the public key. Note: No-one needs someone else's private key. No-one needs two private keys*. *) of course there are practical implementations where organisations use multiple private keys but that is out of scope for this simple case.
-
As for the title of the thread "Can you use traditional cipher be used in public key cryptography?". Assuming @Trurl means symmetric encryption (encryption that lacks public keys) when saying "traditional" then the answer is trivially "yes". The TLS* protocol (earlier versions named SSL) uses public key encryption during handshake to communicate symmetric session keys that are more efficient for the payload traffic. Good question. One reason is edge devices with limited compute power needing secure communication, for instance battery powered devices communicating with cloud services. Looking at statistics (according to google) RSA and Elliptic Curve Cryptography (ECC/ECDSA) run nearly neck-and-neck in active internet SSL/TLS certificate usage. Without interpreting the statistics; short version: Elliptic Curve Cryptography provides same level of security as RSA with shorter keys and with less computation, a possible drawback is there may be compatibility issues with older clients. Side note for the curious: this bash command shows the this forum supports elliptic curves: nmap --script ssl-enum-ciphers -p 443 www.scienceforums.net(the above may require installation on windows. Tested on macOS.) I totally agree. even if (and that is a huge if) the idea would provide a crypto there are other issues such as (not a complete list) -establishing identities: How do I trust the issuer the keys? What is the identity of the sender? (everyone havs the public key). what do I do if the sender claims they did not send a message? What do I do if the private key is stolen? -Text: focuses on text but secure communications needs encrypted traffic regardless of content; documents, images, audio, video, ... -Language: The description does not work for different character sets No such thing exists as far as I know, you seem to be mixing different historical concepts. Scytale is associated with Sparta and is a transposition chipher. Caesar cipher is a substitution cipher associated with Julius Caesar. There are two possible interpretations : 1: your idea describes something that is trivial to decrypt; just by looking at the public key. 2: your idea generates some kind of a lossy encoding, not an encryption. If there is no one to one mapping between plaintext and encryption then no one, not even the intended receiver, can decrypt the message regardless of possession of public, private or both keys. This mans the idea can not be used in the context of encryption. *) "the S in HTTPS" in layman's terms, used heavily in secure internet communication
-
Note to @Trurl if you happen to be on MacOS you can run the bash commands in the terminal directly (openssl is usually preinstalled)
-
You said (bold by me) My comment: If you encrypt with the private key then everyone with the public key can decrypt. There is a use case for encrypting with the private key but it is related to creating and verifying digital signatures. Anyway, This is what you need to describe in more detail. So far the idea you describe makes decryption trivial by using the public key. Note: It is a little confusing; you have two private keys, the public key needs to be created somehow.
-
More details would be required to provide an answer; there seems to be a mixture of encryption, encoding and signing in your post. That defeats the principal property of public-key encryption. Encryption: plaintext --recipient's public key--> ciphertext ciphertext --recipient's private key--> plaintext Signature: message --signer's private key--> signature message + signature --signer's public key--> valid / invalid Encoding: data --encoding rules--> encoded data encoded data --decoding rules--> data
-
What happened evolutionary? Do you imagine a "flick of switch" moment or are there intermediate or overlapping steps to be found? I think the thread contains many confusions about LLM; the discussion might benefit from using the term LLM for what it means; large language model? You seem to mix the properties of an application that is using an LLM (such as Copilot or ChatGPT) with the LLM. The surrounding application may hold conversational state, execute tools, retrieve information, maintain memory, or run generated code. The language model (LLM) typically contains static weights and it processes input only when an inference runtime executes its defined operations. An LLM may behave (very) different depending on surrounding application and state. Or in the case of machine learning or Generative AI based on LLM; we select the wrong training data or training set, select the wrong model (LLM) for the task, misconfigure parameters, have inadequate resources for running the model, wrong quantisation, wrong in destillation, bad fine tuning (and probably many others)
-
Two corrections: That is incorrect in the context of computer science . You can often rewrite, refactor, translate, or optimize a program while preserving its behavior. Compiler optimizations are also semantics-preserving transformations. In computer science; "procedural" has specific meaning. A counter example; SQL. Procedural languages such as C describe how things should be done. SQL is nonprocedural and describes what should be done. (Note: I do not know in the more general sense how your labels “symbolic” and “procedural” map onto established science; I comment only from computer science perspective.)
-
Counterexample: Small children can form friendships. It can be based on for instance play, being close, liking and interaction. All without sharing any “noble goal”.
-
As far as I know there is no inertial frame in which a photon is at rest, and questions about "on his own clock" or what a photon “experiences” do not make physical sense.
-
The chosen corpus appears to be the author’s own theory. If the goal is to evaluate the AI as a science communication tool, why not test it on established, broadly accepted science where independent ground truth exists?
-
No, as pointed out above . My heuristic: Whiteout any scientific evidence I would say that any human skeleton exceeding 280vm in length is a fake.
-
Haven't thought this through but that policy makes them vulnerable to future attacks; an attacker picking off their customer's until there's no business* left? Anyway thanks for the swift action and Merry Christmas! *) Including both software and hosting
-
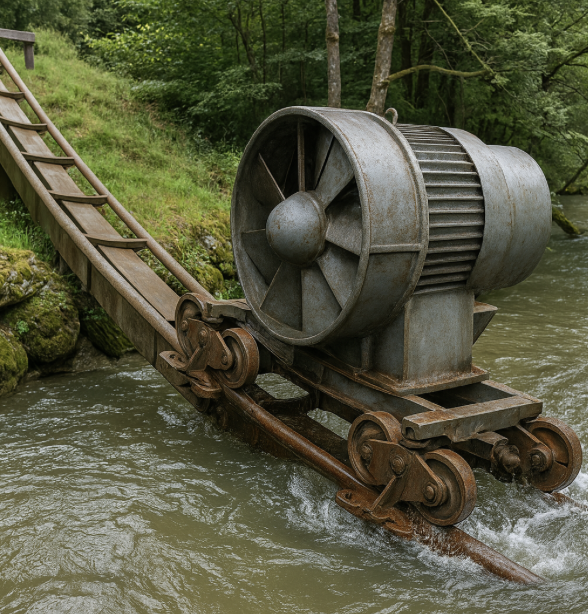
Resizing the turbine after rotating, before submitting it to AI? Example; not 10 meters but bigger that before:
-
I have provided you with an animation and reference images that, to the best of my ability, adhere to established scientific models.* Could you now supply an animation or a mathematical model of the theory or idea you are promoting here? *) I acknowledge that my version is a simplified representation and has not undergone any formal review.
-
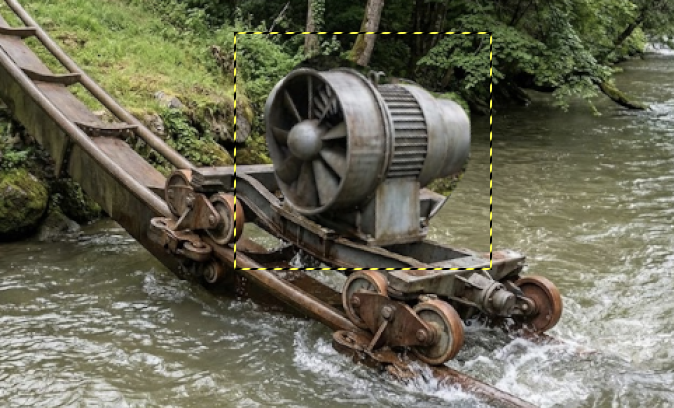
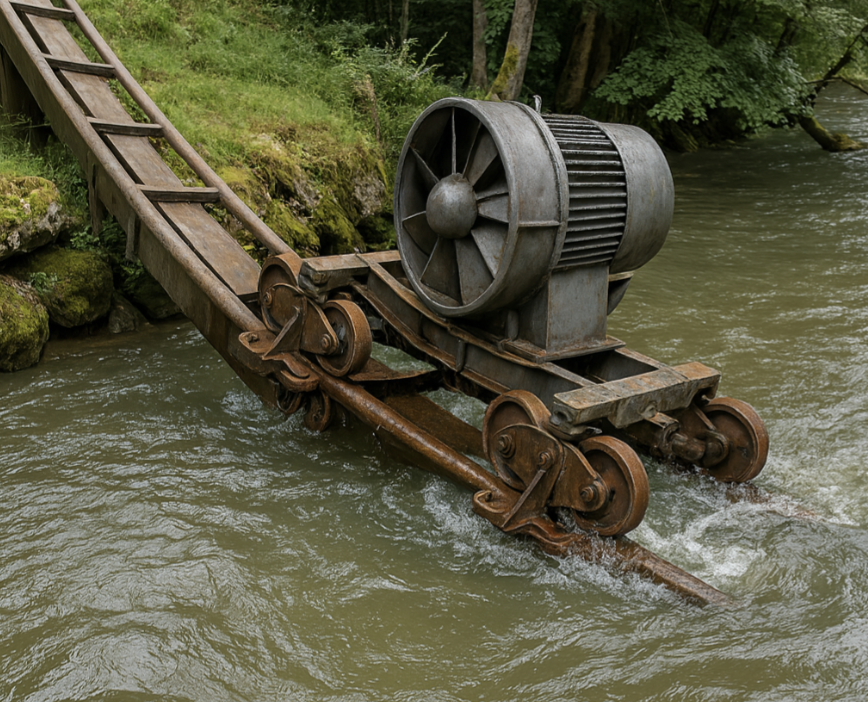
The photographer that took the photo that the model was trained on? More seriously; difficult to provide a generally applicable answer. It may differ between regions, product lines, license etc. Short answer, for a few services I am familiar with, you own the output the AI generates. Issues may involve if the AI outputs very similar images for several users or if output includes other copyrighted material. That is a good suggestion since the model may have limitations of analysing its own output. A prompt "rotate 90 degrees" may cause issues if the model does not manage to grasp what to use as a reference. @Externet this is a case where prompting have limited success; there may not be many similar constructions in the training data. If the AI tool allows you may experiment with uploading references or modifying the image in an image editor and then submit it to AI for "cleaning". Example: I rotated the turbine manually in an image editor. No need to be precise; there are artefacts. Submit the above image to AI, prompting something like "just clean up this picture a little bit" Result: (If more control is required there are the concepts of control nets and similar, but that may require local installations, configurations etc. I'll can provide some links if interesting.) Note @Externet from the title I got the impression you wanted to use ChatGPT; the cleaned up image above was created using ChatGPT, model GPT 5.1
-
You need to be more specific. Also: your description of light and of Ole Rømer’s observations deviates significantly from the established sources. Could you explain what personal idea or hypothesis you are pursuing that leads you to this different interpretation?
-
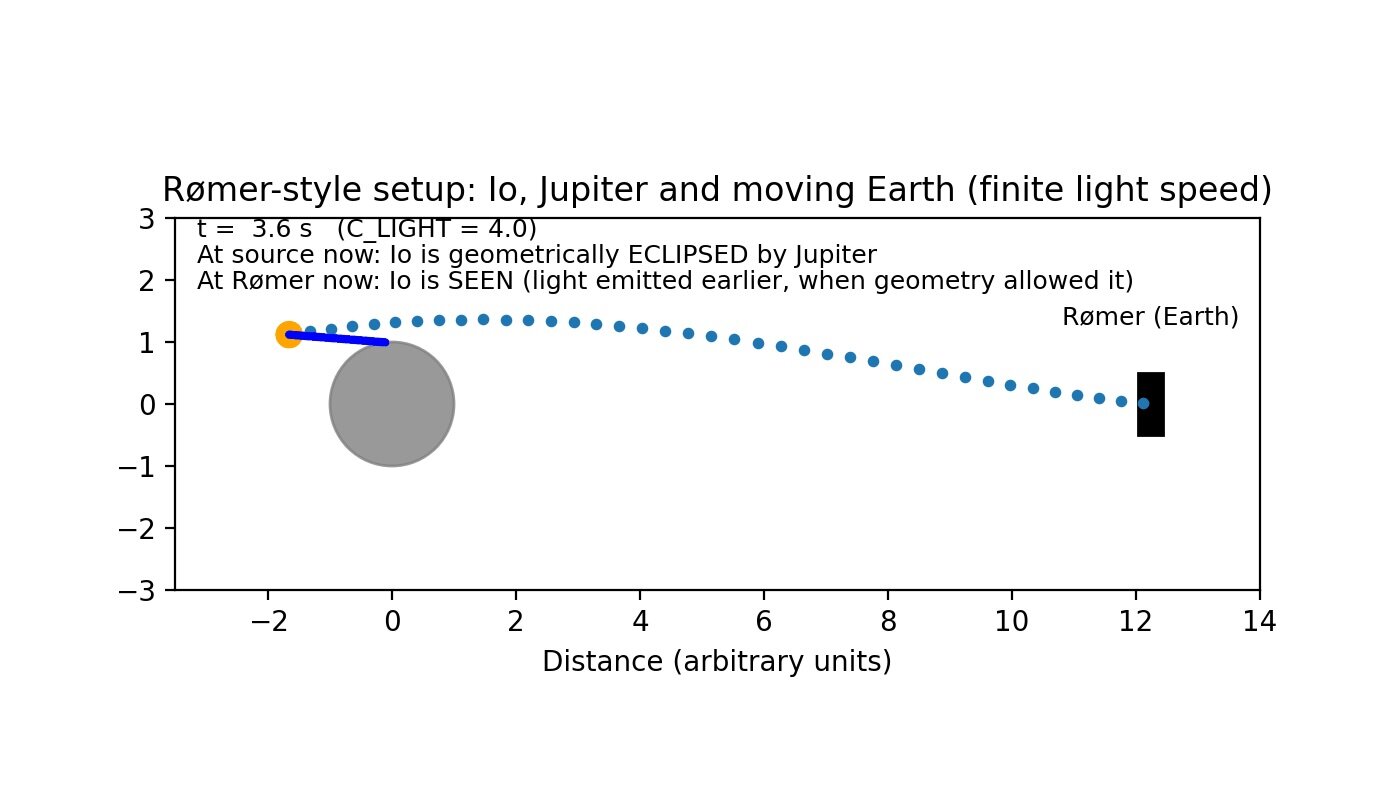
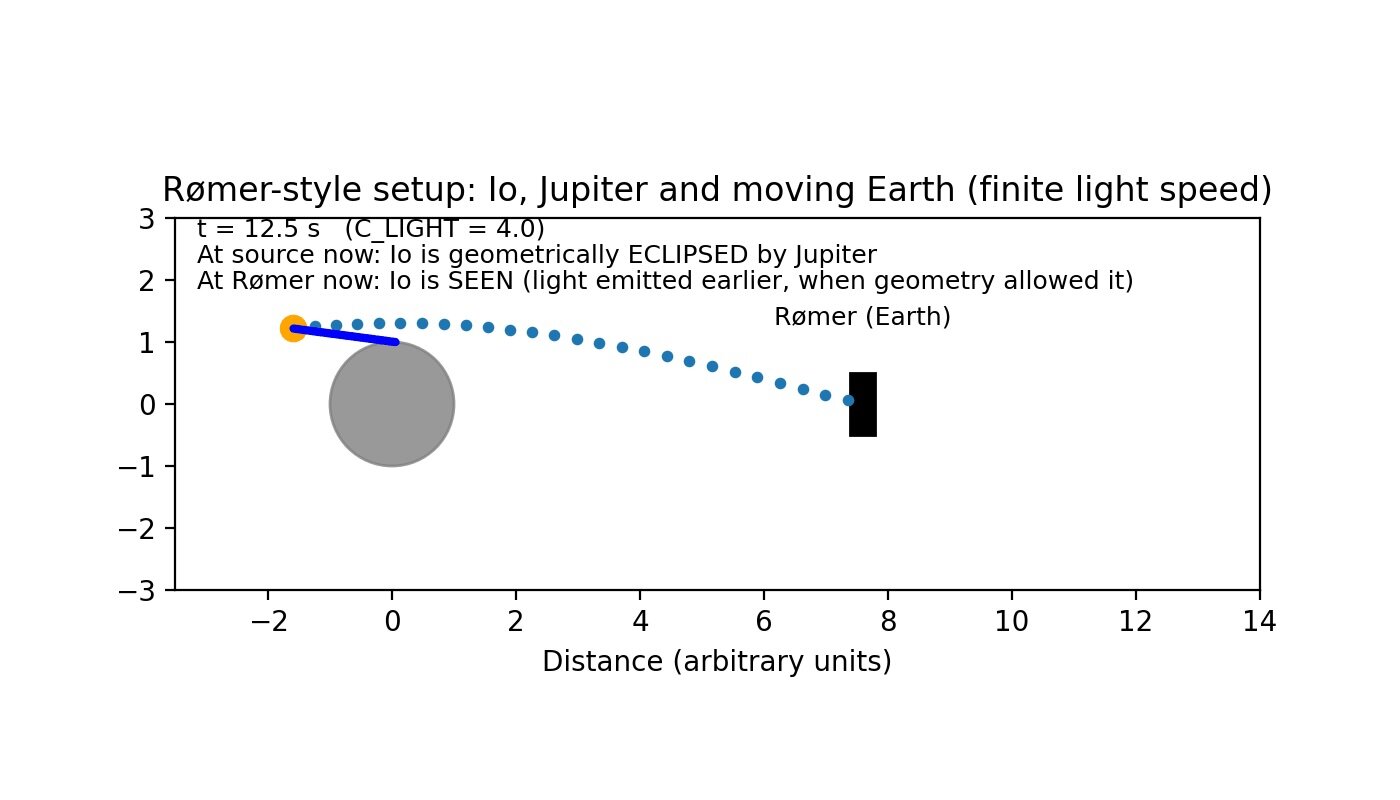
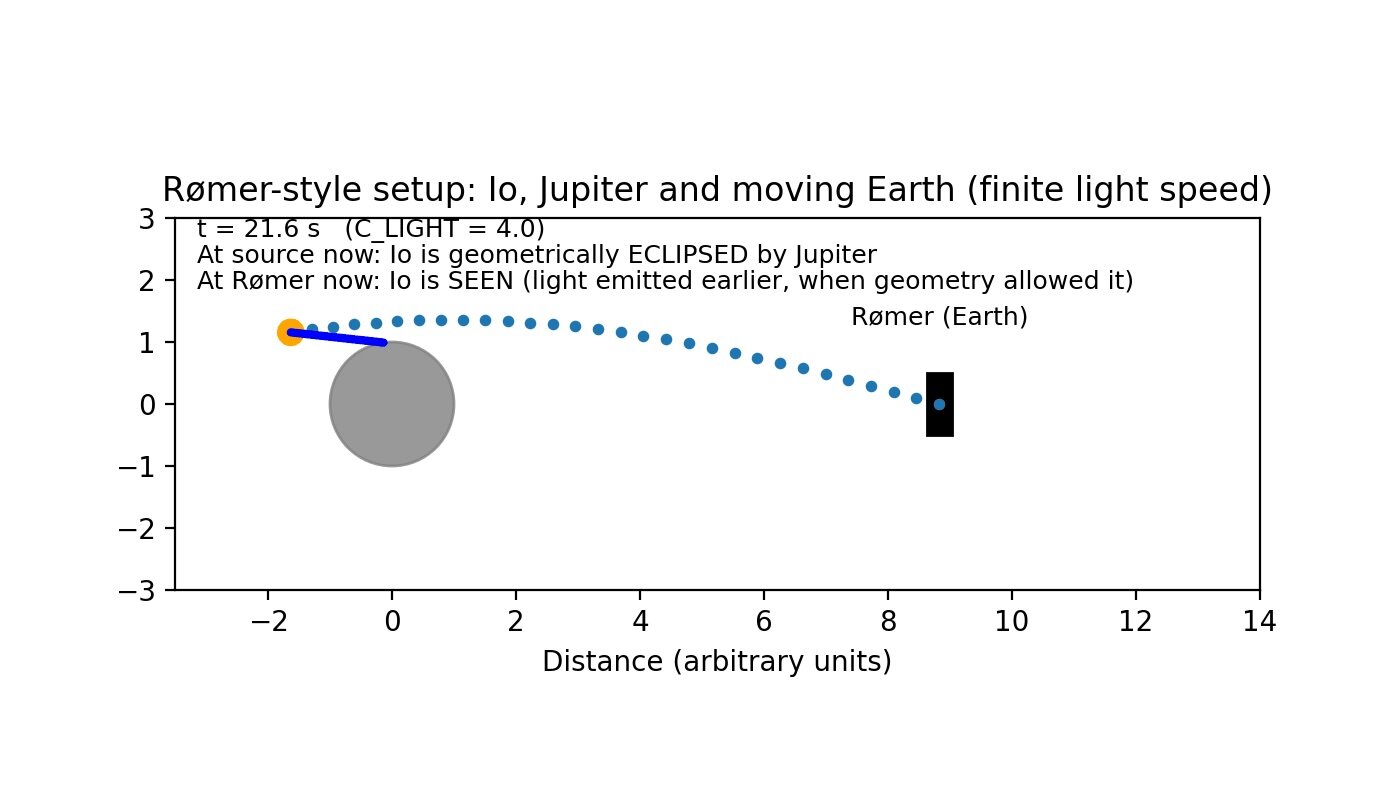
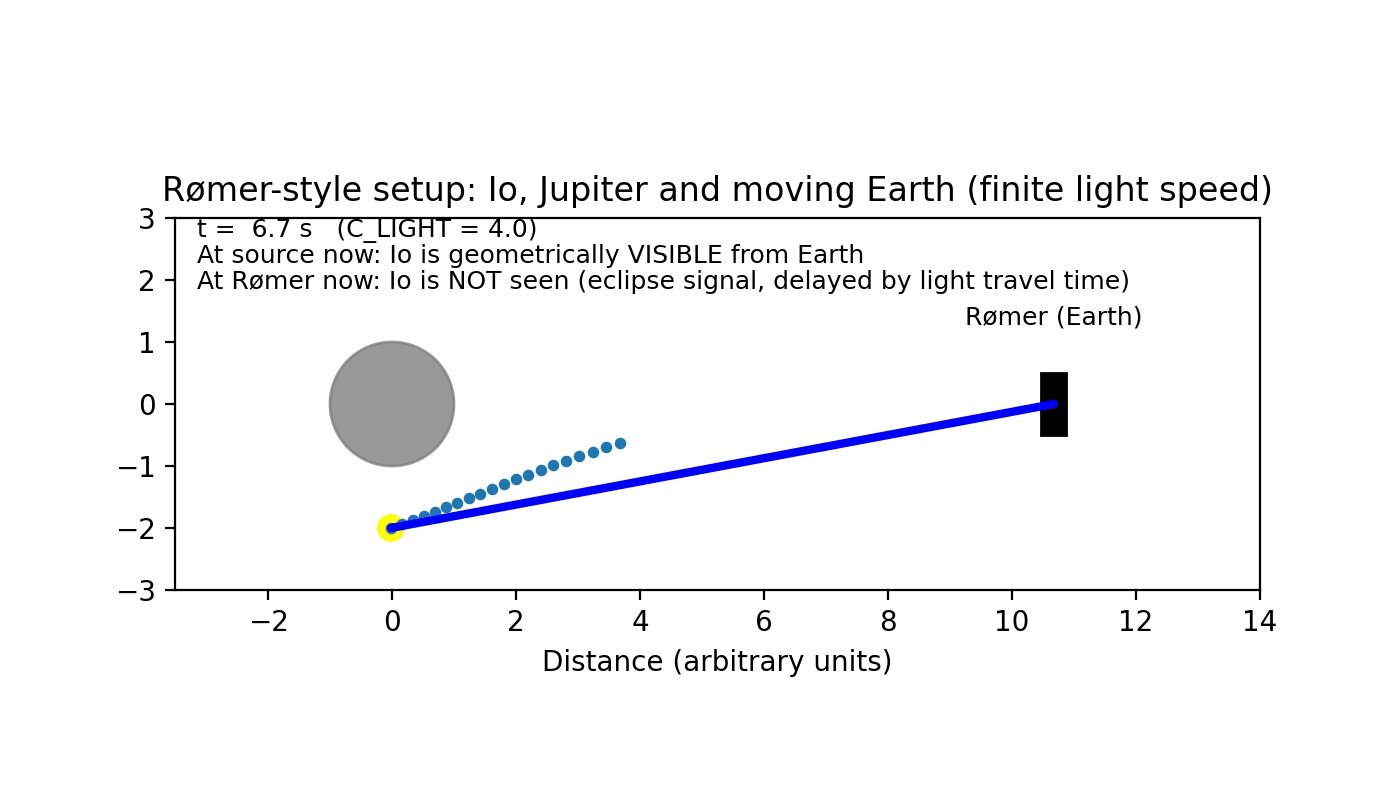
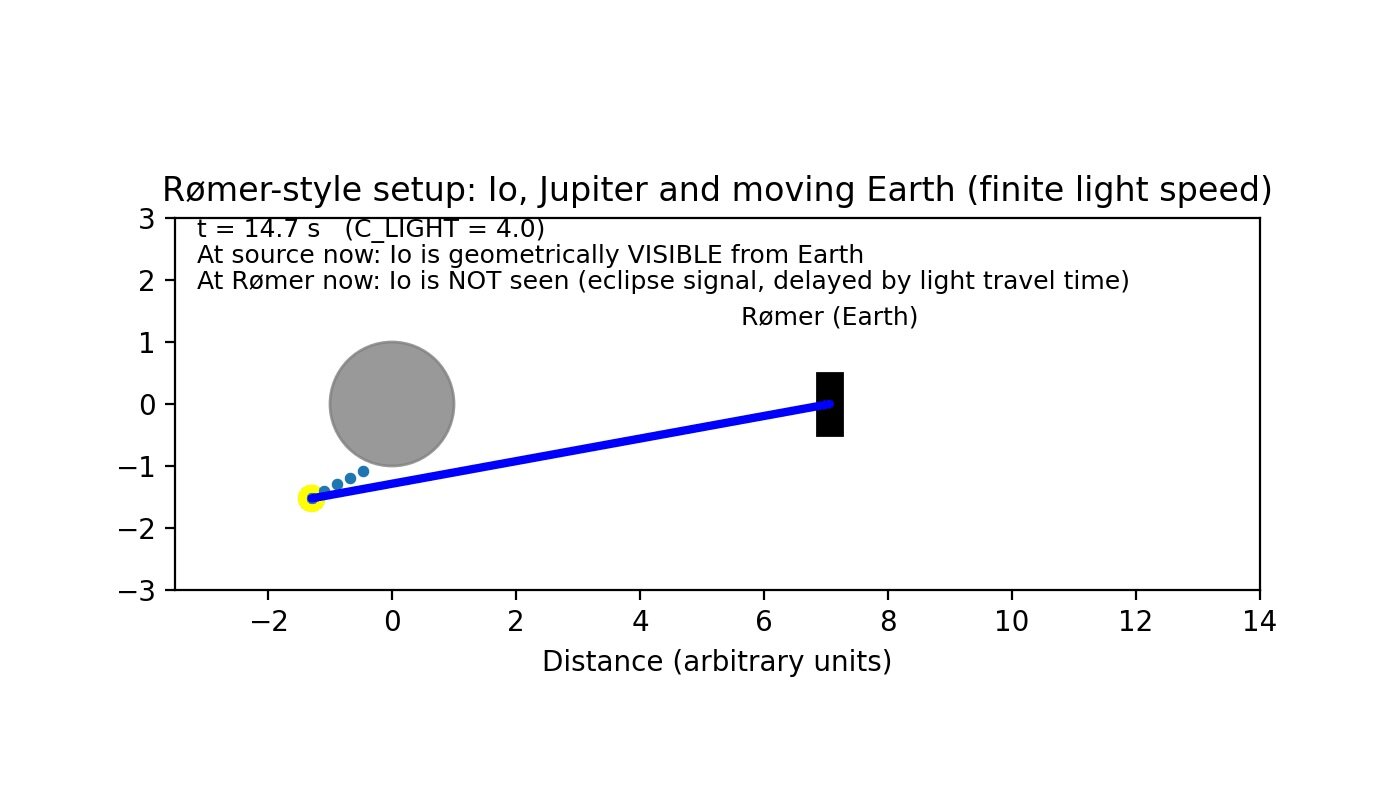
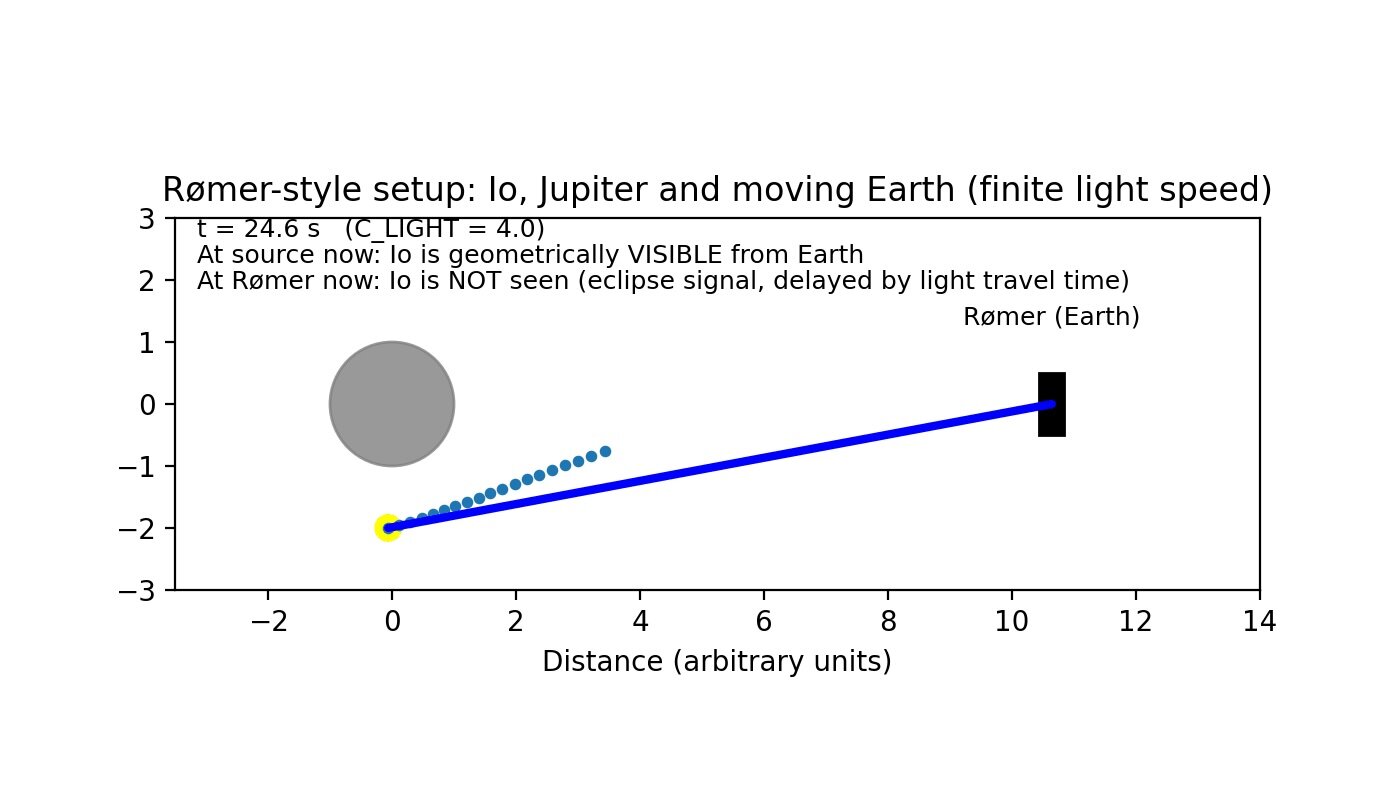
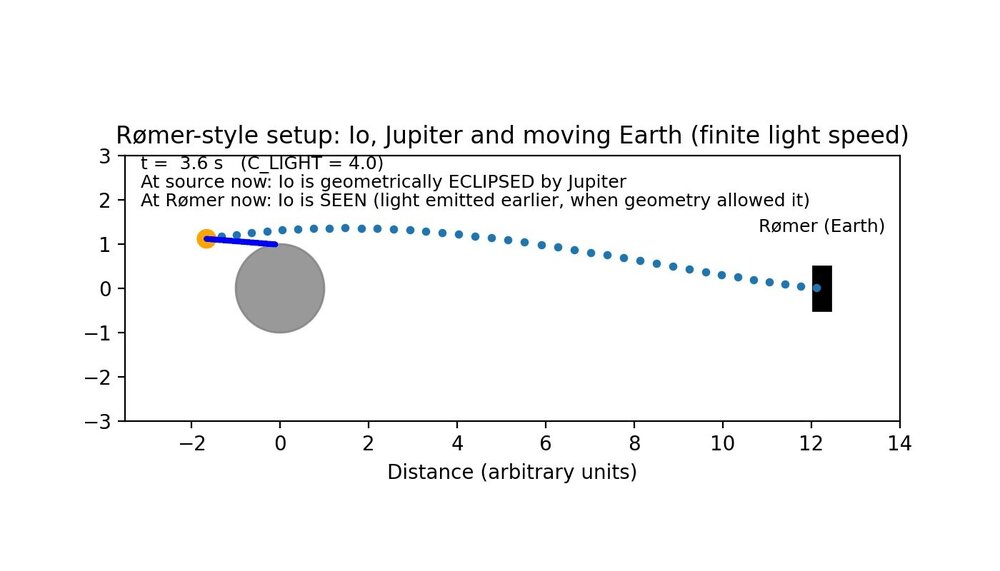
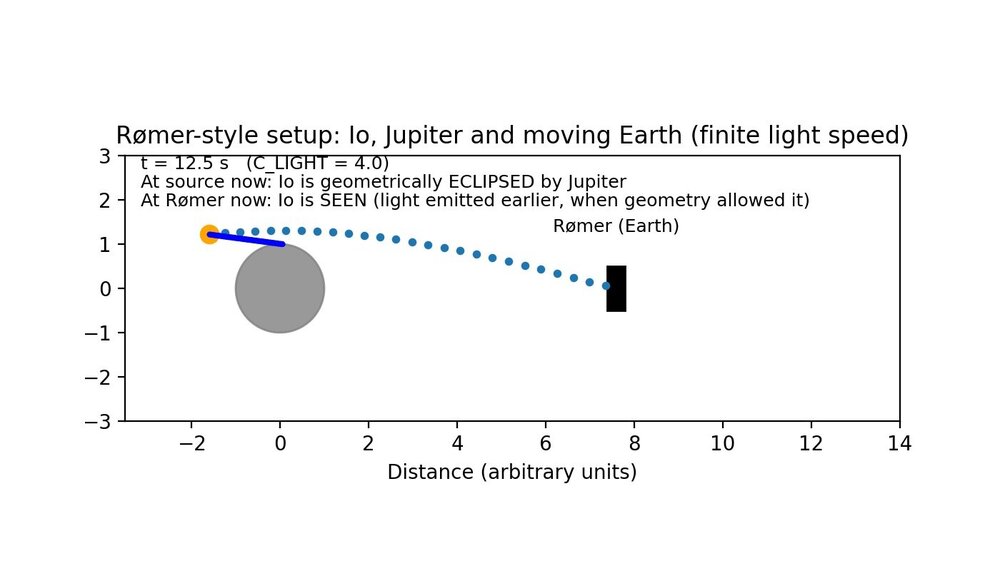
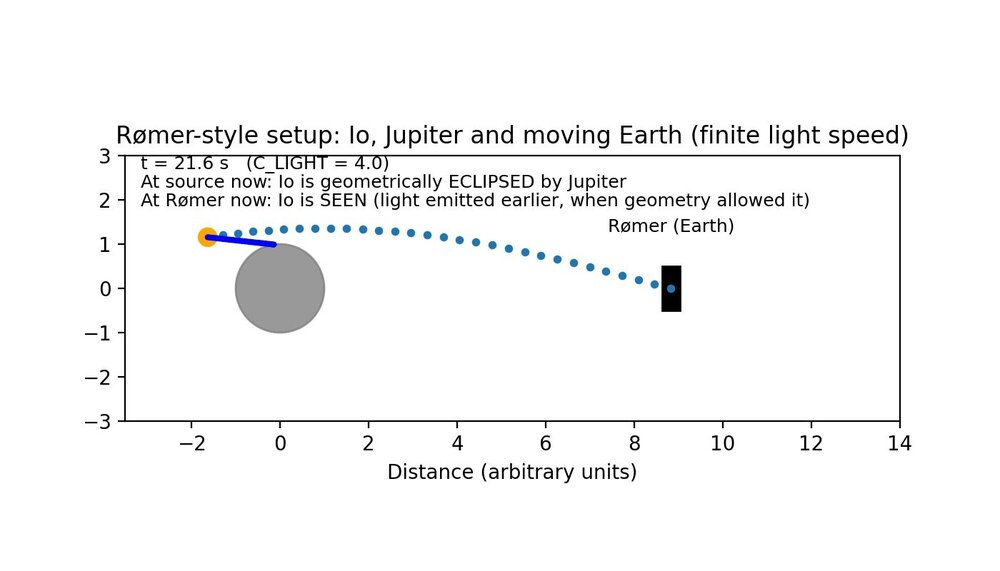
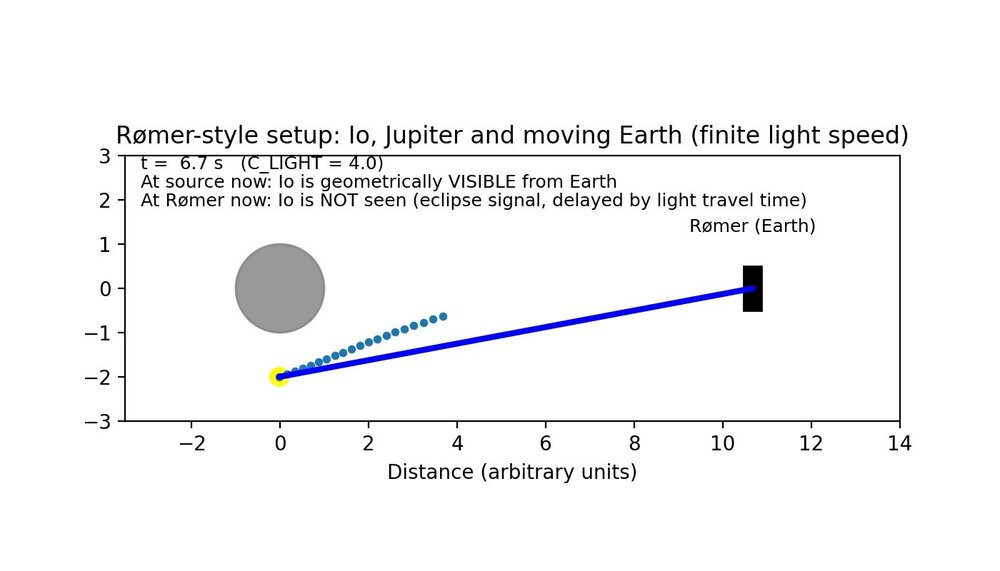
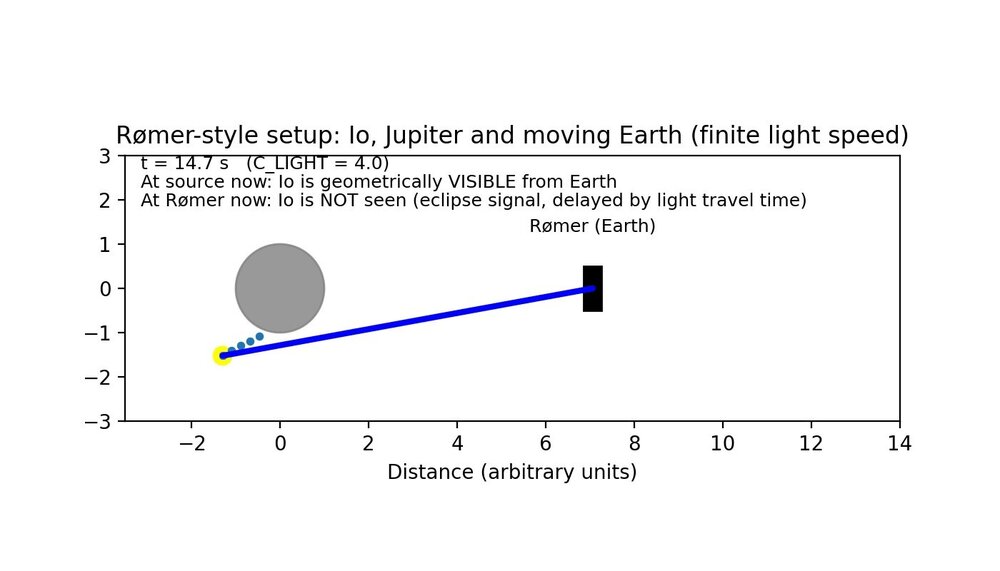
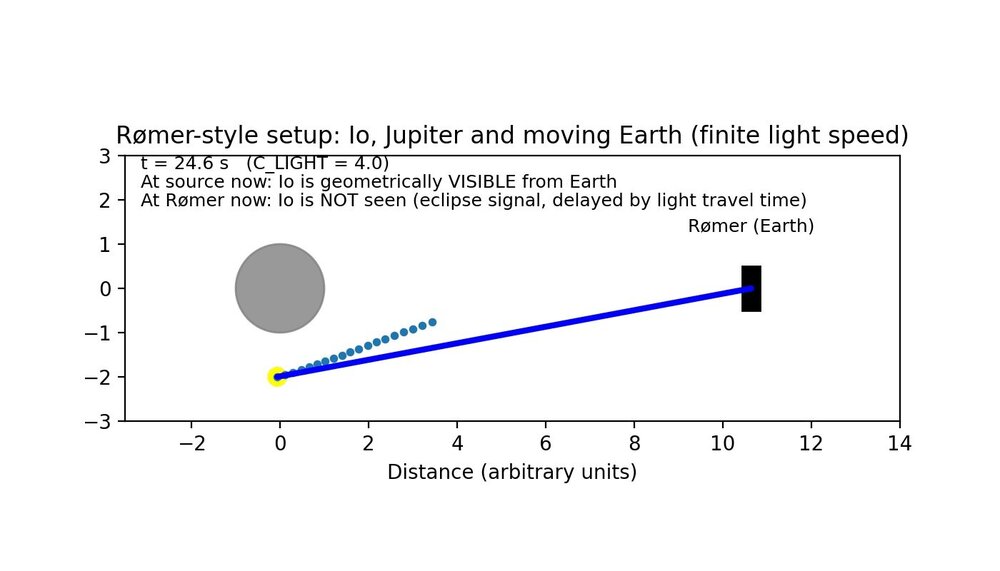
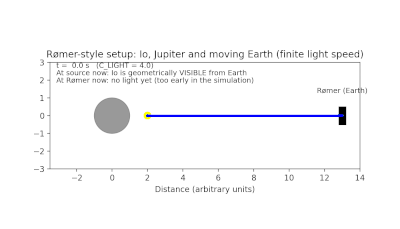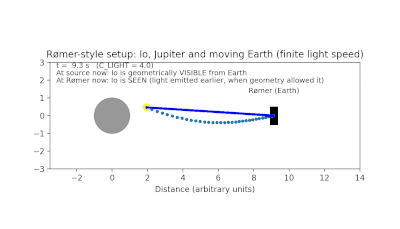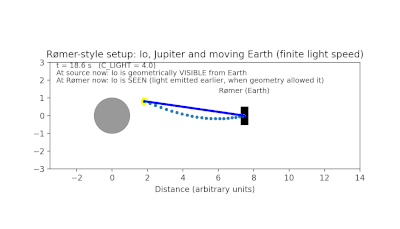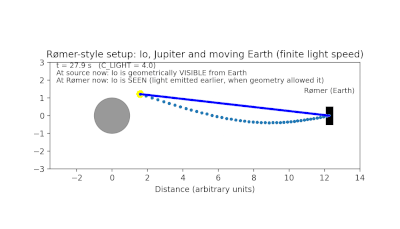
Using your words: "I have given you a map. That map is right in front of you." Look at the timestamps when IO moves behind Jupiter; the moment when there is no line of sight: The timestamps have a consistent interval, IO moves in behind Jupiter every 9nth second. Let's look at time stamps and interval from Rømer's position: These frames are from the point where he observes that IO disappears; no light reaches him from IO. The timestamps does not have a consistent interval, the interval between 1st and 2nd time is 8 seconds and between 2nd and 3rd time it is 9.9 seconds. This illustrates what @swansont and others already said:
-
@jalaldn I have added the observer movement back and forth for you: Fair point; I kept it simple. New version posted.
-
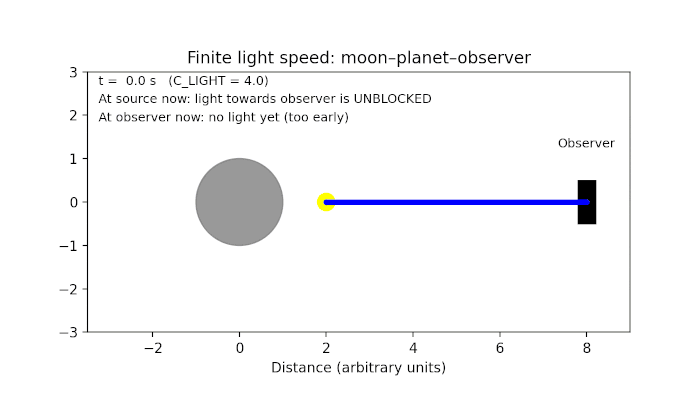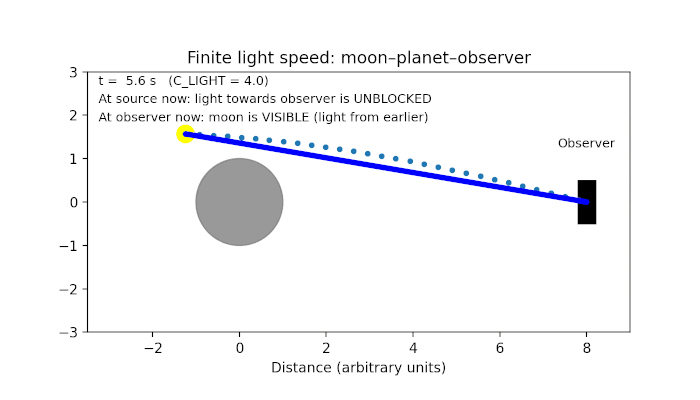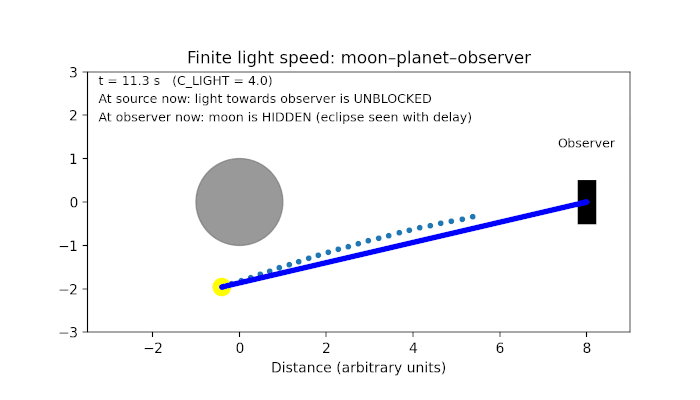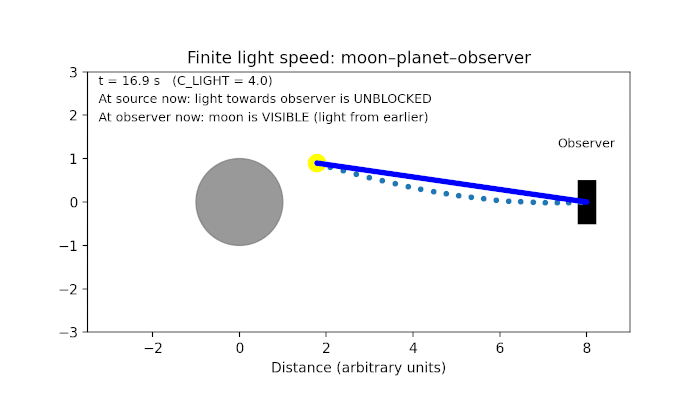
@jalaldn here is a crude animation, maybe this helps. The blue line illustrates line of sight between a moon and a remote observer. The moving dots illustrate photons in transit. Photons hitting the back side of the planet are not included. Note that the blue line is for illustration; there is of course no real time "connection" between observer and moon. In case you missed it: